Demo mode Fictional data · Pro organization · nothing is saved
↻ Restart the tour Request access →
🔐
Logged in as: Alex Demo (alex@demo-league.gg)
🖥️ Machine ID: demo-a1b2c3d4 | 🌐 IP: 10.0.0.42 | ⏰ Last login: 20/09/2026 16:22

📋 #1017 — Havoc_demo

Ended
📅 Calculating... 📦 v1.6.0 💻 5f7a9c1e3b5d… 🌐 10.20.41.75 🎮 Group B · Round 4 🎮 Match ON 💬 havoc.demo

🛡️ Windows Security Modules

Secure Boot
VT-x/AMD-V
Memory Integrity (HVCI)
Vulnerable Driver Blocklist
IOMMU/VT-d (info) ⚠️
Virtualization Detected

📊 Data completeness v1.1.3+

Drivers
143
Registry
12
Overlays (scanned: 17)
2
Game DLLs (analyzed)
96
Filesystem scan (OK)
0
UDP
6
🔍

⚠️ HUMAN REVIEW REQUIRED

Reason: Very low score (33) — degraded profile, manual review required

⏳ Pending staff review

🤖 Confidence Score (AI)

33
🔴 High Risk

⚠️ Penalties (3)

Unsigned executable (user-writable path) -25 pts
Suspicious overlay detected -20 pts
Security module disabled -12 pts

⭐ Bonus (1)

Recognized gaming tool (informational signal) +1 pts
ℹ️ Analyzed on • Phase 2 • Calculation time: 6120ms
🤖

AI Analysis PRO

Provider: Gemini • Confidence: MEDIUM
Adjusted score:
41 33 (-8 pts)
🚩 Suspicious points
  • Unsigned executable launched from %TEMP% with admin elevation, 4 min before the match
  • Clickthrough overlay window owned by that same process, visible for 9 min during map 2
  • HVCI disabled: one less layer of protection against unsigned code
✅ Mitigating factors
  • No known cheat signature, no cheat hardware detected
  • Discord overlay identified separately and legitimate
  • The player's previous 4 sessions were clean
🔍 Detailed analysis of each element
⚙️ svc_update.exe (Process)
⚠️ Suspicious Confidence: HIGH

💬 Name mimics an update service, but it runs from a temp folder, is unsigned and elevated. Real updaters run from Program Files and carry their publisher's signature.

⚙️ svc_update.exe [1920x1080]+clickthrough (Overlay)
⚠️ Suspicious Confidence: MEDIUM

💬 Transparent full-screen window above the game, matching no known streaming or clipping tool. Visible from the 9th to the 18th minute, during map 2.

⚙️ Discord.exe (overlay) (Process)
✅ Legitimate Confidence: HIGH

💬 Standard Discord overlay, present on most of the organization's sessions.

⚙️ Memory Integrity (HVCI) (Security)
⚠️ Suspicious Confidence: LOW

💬 Disabled. Common among players who overclock their mouse or controller — a weak signal on its own, but it adds weight combined with the two points above.

AI recommended action: (⚠️ Overridden by Rule Engine)
🔍 Manual review
ℹ️ Final decision: Human Review Required (Rule Engine)

💬 AI Conversation PRO

AI analysis summary
🤖
Gemini · 19/09 20:28
Ask the AI a question about this session...
In the demo the chat is simulated: pick a question below. With a real account you ask anything and the AI answers from the session's actual data.
Suggested questions
Enter to send · Shift+Enter for new line

⚠️ Alerts for this session (3)

Severity Type Details Date Resolved on Action
HIGH 🖼️ Suspicious overlay 🖼️ Suspicious overlay detected
• svc_update.exe [1920x1080]+clickthrough
-
HIGH ⚠️ Suspicious process ⚠️ svc_update.exe -
MEDIUM 🔓 Hardware security disabled 🔓 Memory Integrity (HVCI)
Security module disabled
-

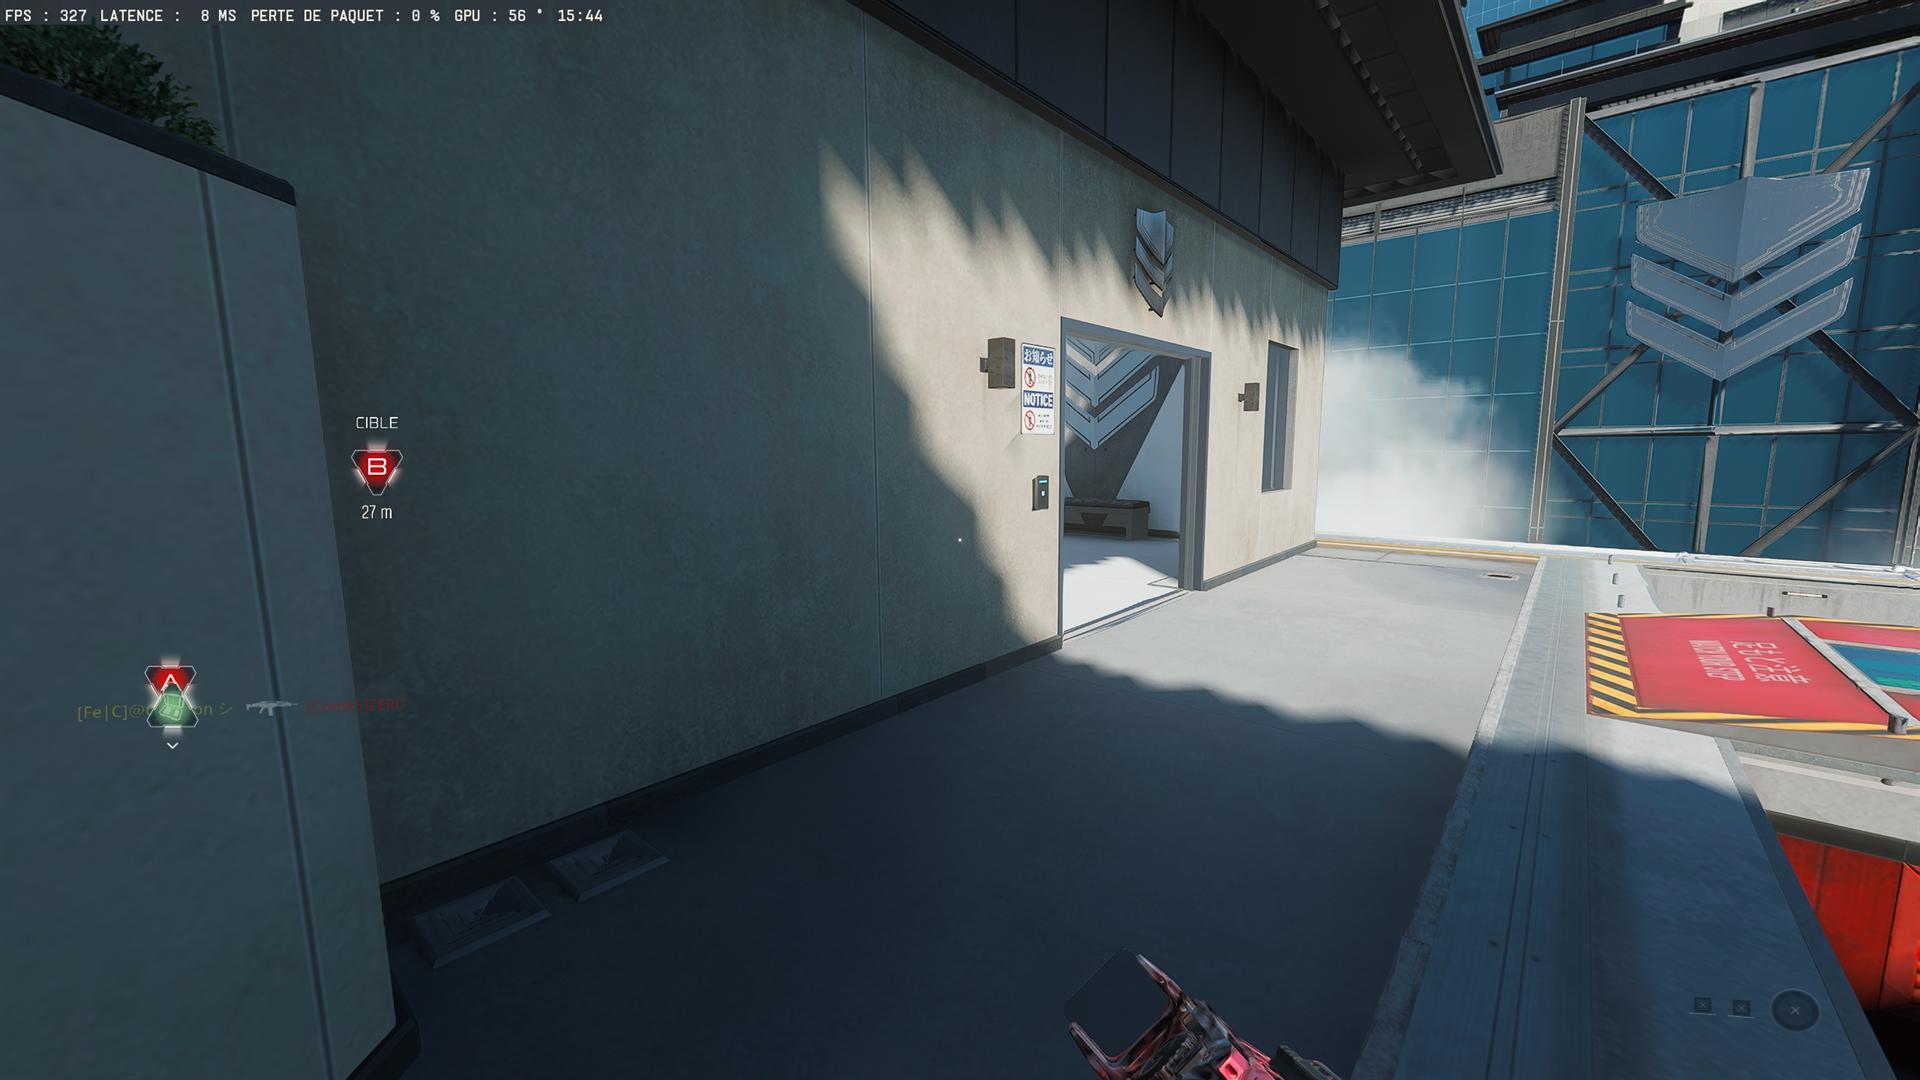
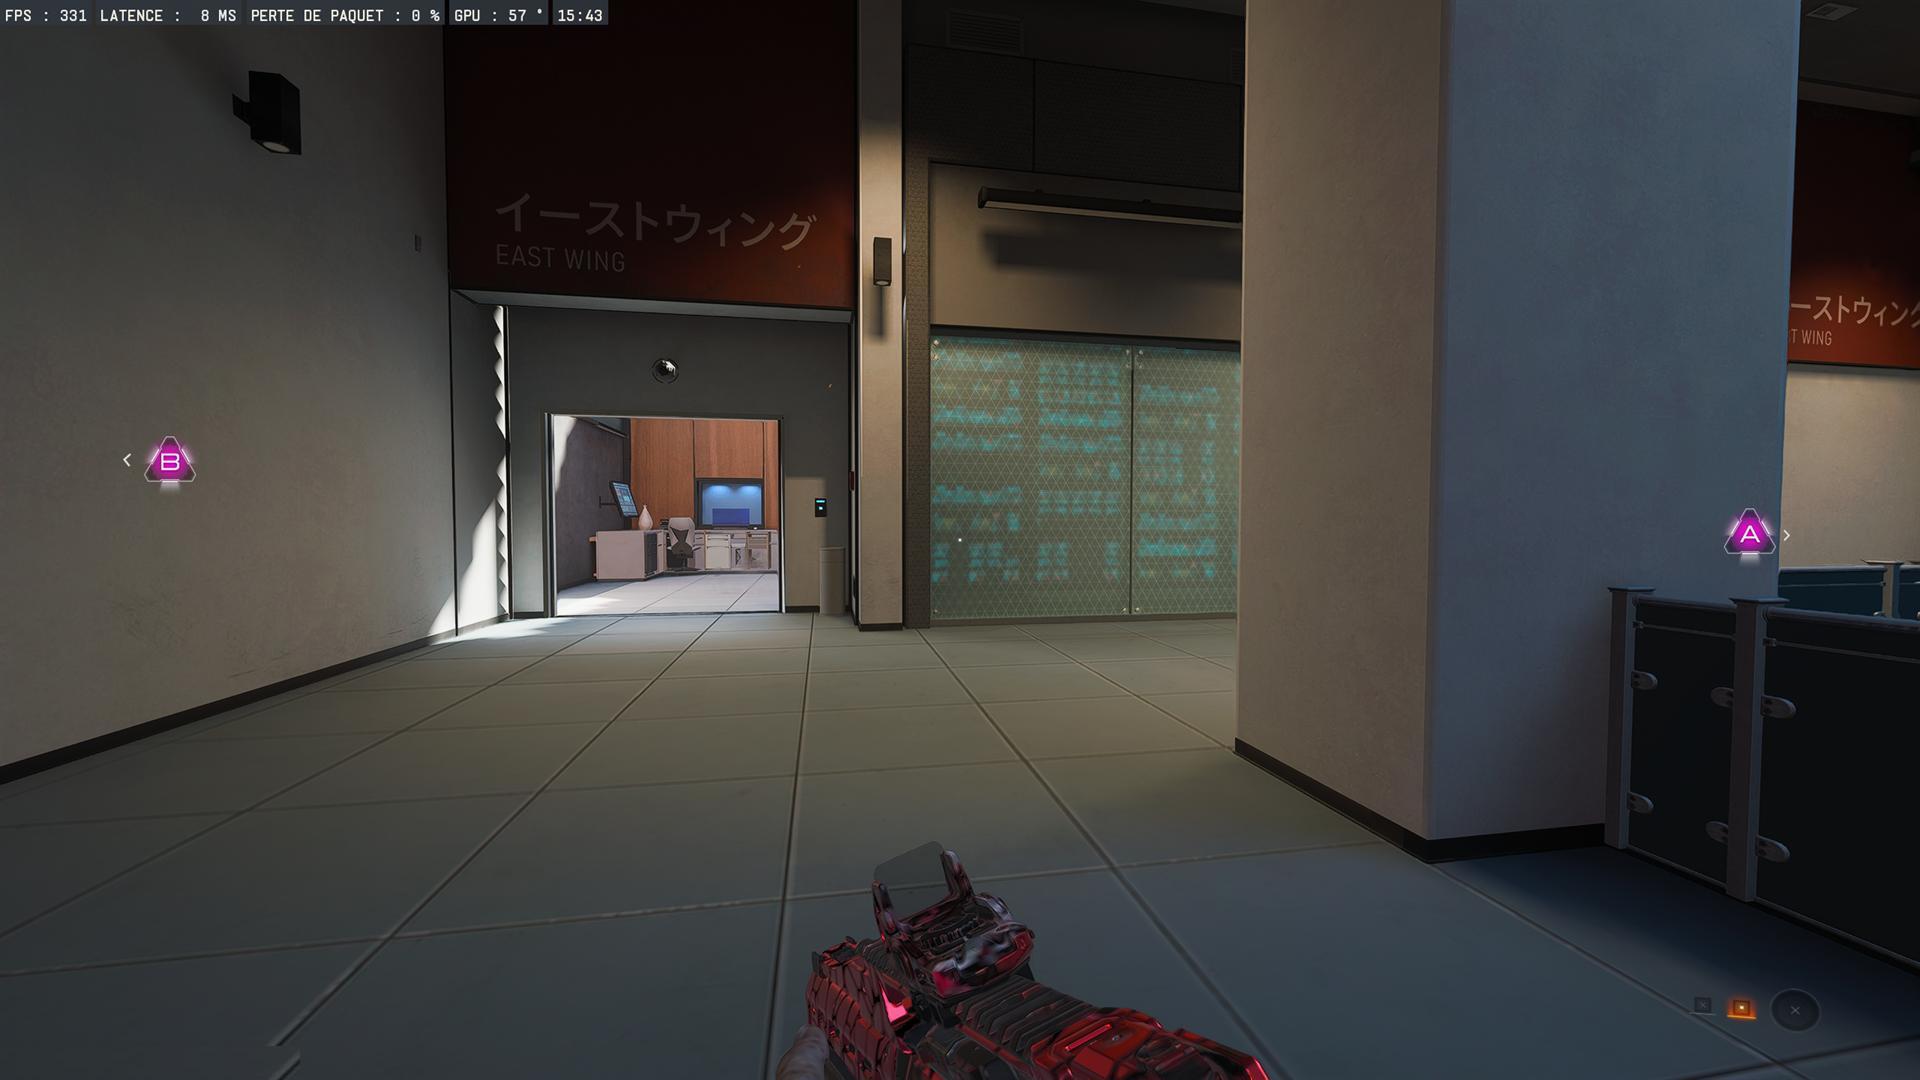
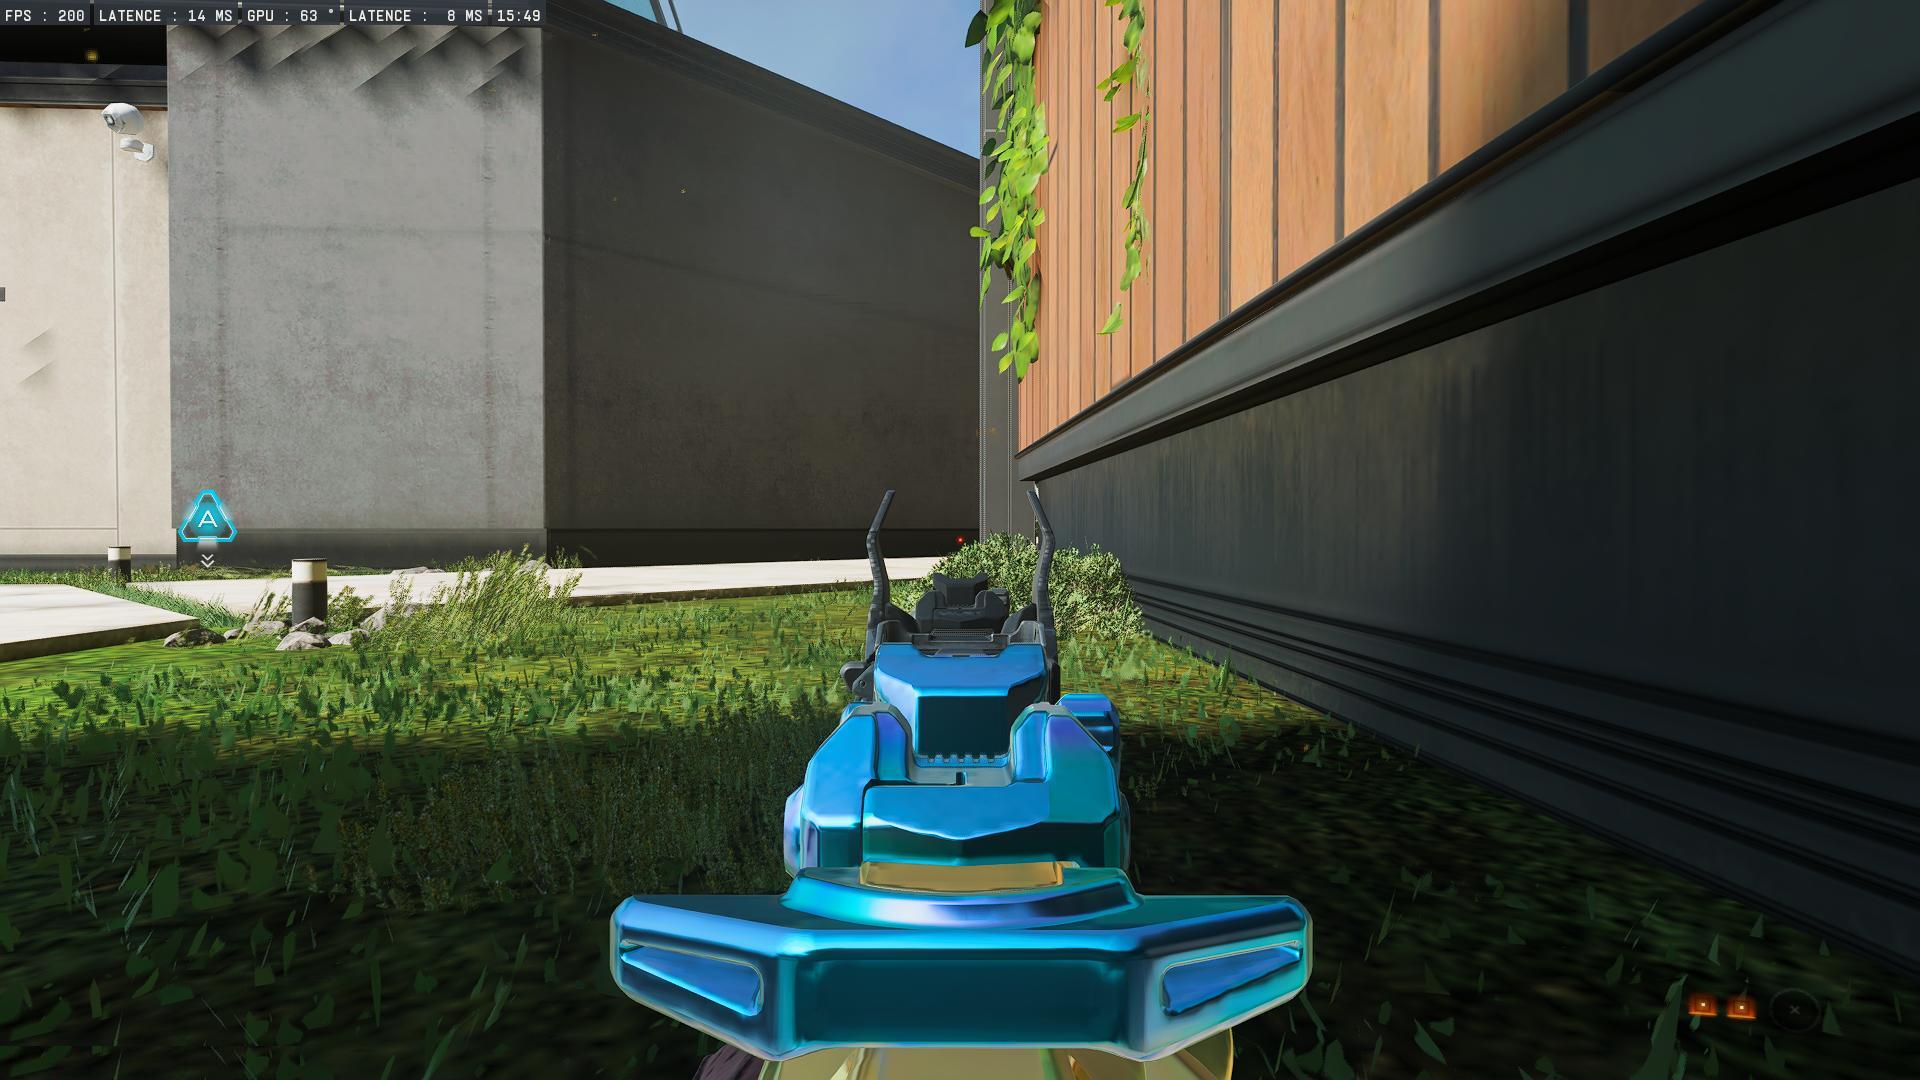
📸 Screenshots (11)

Screenshot Screenshot
🖥️ 2 screens · 458.3 KB GDI
Screenshot Screenshot
🖥️ 2 screens · 430.1 KB GDI
Screenshot Screenshot
🖥️ 2 screens · 526.7 KB GDI
Screenshot Screenshot
🖥️ 2 screens · 462.9 KB GDI

🖥️ Configuration PC

Operating system
Microsoft Windows 11 Pro
Build 22631 · 64-bit · UEFI
Locale : fr-FR · Uptime : 412 min
Installed : 2025-11-03
CPU
Intel(R) Core(TM) i5-13600K
14 cores / 20 threads · 3500 MHz
GenuineIntel
Motherboard
MAG B760 TOMAHAWK WIFI
Micro-Star International Co., Ltd.
Rev : 1.0 · S/N (h): c71d…04ab
BIOS / UEFI
1.70
American Megatrends International, LLC.
Date : 2024-03-21 · SMBIOS 3.5
Memory
16 GB
2 module(s) · 5600 MHz
GPU
NVIDIA GeForce RTX 3070
Driver 552.44
System disk · 2 physical
931 GB · NVMe
BitLocker : ⚪ disabled
All physical disks (2)
NVMe KINGSTON SNV2S1000G
HDD (SATA) ST2000DM008-2FR102
TPM
✅ · v2.0
Identifiers (SHA-256 hashed)
hostname : a3f9…c12e
username : 7b21…e04d
MAC(s) : 91cf…3a8b
Collected 2026-09-19 19:14:45 · WMI : 412ms · collector v3

💻 Device history (8 unique)

🖥️ Screen configuration: 2 screen(s) - 2560x1440 / 2560x1440
Show/Hide devices (8)
Type Name ID/VID:PID Manufacturer Connection Status
HID Razer DeathAdder V3 Pro 1532:00B7 Razer ⏏️ ✓ OK
HID Logitech G Pro X Keyboard 046D:C339 Logitech ⏏️ ✓ OK
Audio SteelSeries Arctis Nova Pro 1038:12CB SteelSeries ⏏️ ✓ OK
HID Xbox Wireless Controller 045E:0B12 Microsoft ⏏️ ✓ OK
Display ASUS ROG Swift PG279QM AUS27B1 ASUS ⏏️ ✓ OK
Display Dell U2722D DEL41F5 Dell ⏏️ ✓ OK
Camera Logitech BRIO 046D:085E Logitech ⏏️ ✓ OK
Storage Samsung Portable SSD T7 04E8:4001 Samsung ⏏️ ✓ OK

🔍 Session process history (25 unique) (1 suspect(s))

📋 Show/Hide processes (25)
⚠️ svc_update.exe HIGH ADMIN
C:\Users\Player\AppData\Local\Temp\svc_update.exe
Unsigned executable (user-writable path)
cod.exe
C:\Program Files (x86)\Steam\steamapps\common\Call of Duty\cod.exe
steam.exe
C:\Program Files (x86)\Steam\steam.exe
steamwebhelper.exe
C:\Program Files (x86)\Steam\bin\cef\cef.win7x64\steamwebhelper.exe
Discord.exe
C:\Users\Player\AppData\Local\Discord\app-1.0.9165\Discord.exe
chrome.exe
C:\Program Files\Google\Chrome\Application\chrome.exe
NVIDIA app.exe
C:\Program Files\NVIDIA Corporation\NVIDIA app\CEF\NVIDIA app.exe
nvcontainer.exe
C:\Program Files\NVIDIA Corporation\NvContainer\nvcontainer.exe
RazerCentralService.exe
C:\Program Files (x86)\Razer\Razer Services\Razer Central\RazerCentralService.exe
lghub.exe
C:\Program Files\LGHUB\lghub.exe
Spotify.exe
C:\Users\Player\AppData\Roaming\Spotify\Spotify.exe
explorer.exe
C:\Windows\explorer.exe
dwm.exe
C:\Windows\System32\dwm.exe
svchost.exe
C:\Windows\System32\svchost.exe
RuntimeBroker.exe
C:\Windows\System32\RuntimeBroker.exe
SearchHost.exe
C:\Windows\SystemApps\MicrosoftWindows.Client.CBS_cw5n1h2txyewy\SearchHost.exe
MsMpEng.exe
C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.24090.11-0\MsMpEng.exe
OneDrive.exe
C:\Users\Player\AppData\Local\Microsoft\OneDrive\OneDrive.exe
audiodg.exe
C:\Windows\System32\audiodg.exe
SkedacAntiCheat.exe
C:\Program Files\SkedAC\SkedacAntiCheat.exe
Overwolf.exe
C:\Program Files (x86)\Overwolf\Overwolf.exe
SteelSeriesGG.exe
C:\Program Files\SteelSeries\GG\SteelSeriesGG.exe
ctfmon.exe
C:\Windows\System32\ctfmon.exe
taskhostw.exe
C:\Windows\System32\taskhostw.exe
conhost.exe
C:\Windows\System32\conhost.exe

📝 Admin notes for Havoc_demo (0)

No notes for this player